Posts

AWS: Initial Documentation

Image
          What is Baseline configuration page in technical terms? - The baseline configuration page serves as a cornerstone for company associates, guiding them through the intricacies of AWS cloud services. Understanding the baseline configuration is akin to possessing a compass in uncharted territory it provides direction and ensures a smooth journey through the AWS landscape. Begin with the fundamental AWS IAM configurations. Stress the importance of establishing granular permissions, adhering to the principle of least privilege. A well-defined IAM setup lays the groundwork for secure and efficient cloud operations. Move on to networking essentials, emphasizing the creation of virtual private clouds (VPCs) tailored to specific project requirements. Highlight the significance of subnetting, routing, and security groups in sculpting a robust and isolated network environment. Dive into storage configurations, elucidating the differences between Amazon S3 for sca...

AWS: Cloudfront Distribution

Image
-- What is CloudFront WebAcl ID? A WAF Access Control List (WebACL) ID in Amazon CloudFront is a component for enhancing the security of web applications and content delivery. CloudFront is AWS content delivery network service, and a WebACL ID is used to enforce security rules and policies on incoming traffic to protect against various web threats. The WebACL ID serves as a reference to a specific set of rules and configurations within the WAF service. These rules are designed to filter and inspect incoming HTTP or HTTPS requests, helping to mitigate common web application vulnerabilities such as SQL and more. When configuring CloudFront distributions, users can associate a WebACL ID with a distribution, effectively allowing the WebACL to act as a shield for the content being delivered through CloudFront. This means that incoming requests must pass through the WebACL's rules before reaching the origin server, helping to block malicious traffic and protect against attacks. CloudFron...

AWS: Cloudfront Viewer Policy

Image
--- What is AWS Cloudfront Viewer Policy? The CloudFront Access Viewer is a tool provided by Amazon Web Services (AWS) that allows you to monitor and analyze the usage of your Amazon CloudFront distributions. CloudFront is a content delivery network (CDN) that helps distribute your web content globally with low latency. The Access Viewer provides insights into viewer requests for your CloudFront distributions, showing details such as request methods, response status codes, geographic locations, and more. This tool aids in troubleshooting and optimizing content delivery performance by helping you identify patterns and potential issues. It's particularly useful for understanding how users interact with your content, which can guide improvements to your distribution setup and content delivery strategies. By leveraging the CloudFront Access Viewer, you can enhanc e the overall user experience and ensure efficient distribution of your web content across the globe. --- Python code that u...

AWS: ECS Propagating Tags

Image
-- What is ECS AWS? Amazon Elastic Container Service is a cloud-based container orchestration service provided by AWS. It enables developers to easily deploy, manage, and scale containerized applications using Docker containers. With ECS, users can define and organize their applications into logical units called "task definitions," which specify the required resources and container images. These tasks run on EC2 instances or AWS Fargate, a serverless compute engine for containers. -- ECS Services The service offers a simplified and highly scalable solution for running containers, handling resource provisioning, load balancing, and automatic scaling based on demand. ECS also integrates seamlessly with other AWS services, such as Amazon VPC for networking, IAM for access control, and CloudWatch for monitoring. By leveraging A ECS, developers can focus on their application's functionality without worrying about infrastructure management. Its flexibility, reliability, and tig...

AWS: S3 Tagging

Image
What is S3 Bucket? -- Amazon Simple Storage Service (S3) is a cloud-based storage service provided by AWS. It offers scalable, durable, and highly available object storage, making it a popular choice for various applications, from data backups and content distribution to big data analytics and application hosting. S3 operates on the concept of "buckets," which are containers for storing objects such as images, videos, documents, and other data types. Each object within a bucket is uniquely identified by a key and can be accessed through a URL. It supports various storage classes, allowing users to optimize costs based on data access patterns. These classes include Standard, Intelligent-Tiering, Infrequent Access, Glacier etc. -- To update or append tags in S3 bucket . Python code using the boto3 library to change tags for an object in an Amazon S3 bucket: import boto3 s3 = boto3.client("s3") new_tags = [     {'Key': 'Tag1', 'Value': 'Valu...

AWS: CloudFront Distribution Viewer Policy

Image
What is CloudFront ? -- CloudFront is a content delivery network service provided by AWS. It helps deliver static and dynamic web content, including videos, images, and applications, to end-users with low latency and high transfer speeds. -- CloudFront uses a global network of edge locations to cache and serve content from the location closest to the end-user, reducing the distance and improving overall performance. It also offers features like SSL/TLS encryption, DDoS protection, and integration with other AWS services, making it a popular choice for accelerating content delivery across the globe. Example -- To change the CloudFront viewer policy using boto3 -- CloudFront Distribution Viewer Policy : CloudFront allows you to control access to your content by specifying a viewer policy. The viewer policy defines who can access your content based on various criteria such as IP address, HTTP headers, cookies, and more. It helps you restrict access and implement fine-grained access contro...

AWS: Custom Config Rule

Image
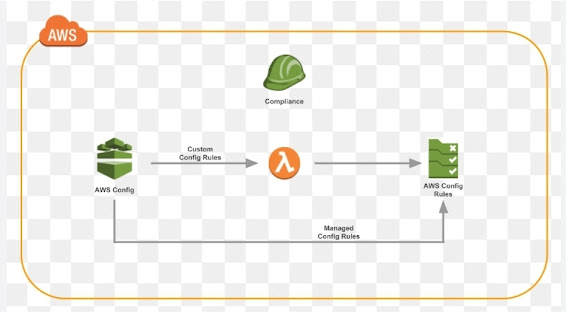
-- Explain Custom config with an example? -- Custom config rules in AWS Config allow you to define your own rules to evaluate the configuration settings of your AWS resources. These rules help ensure that your resources are compliant with your organization's requirements and best practices. A custom config rule is created using AWS Lambda functions that evaluate the resource configurations and return a compliance status. {   "ConfigRuleName": "Sumodh c Sabu",   "Description": "Checks if S3 buckets have server-side encryption enabled.",   "InputParameters": {},   "Scope": {     "ComplianceResourceTypes": [       "AWS::S3::Bucket"     ]   },   "Source": {     "Owner": "CUSTOM_LAMBDA",     "SourceIdentifier": <<arn name>>   } } -- In this example , the custom config rule is named "Sumodh c Sabu" and its purpose is to verify if S3 buckets have se...